Apple will pay you $5,000,000 if you can find bugs in its software
Published on Oct 13, 2025 at 5:51 AM (UTC-4)
by Molly Davidson
Last updated on Oct 13, 2025 at 12:04 PM (UTC-4)
Edited by
Emma Matthews

The Apple bug bounty just got turbocharged.
The company is about to start handing out the kind of money usually reserved for lottery winners… not hackers.
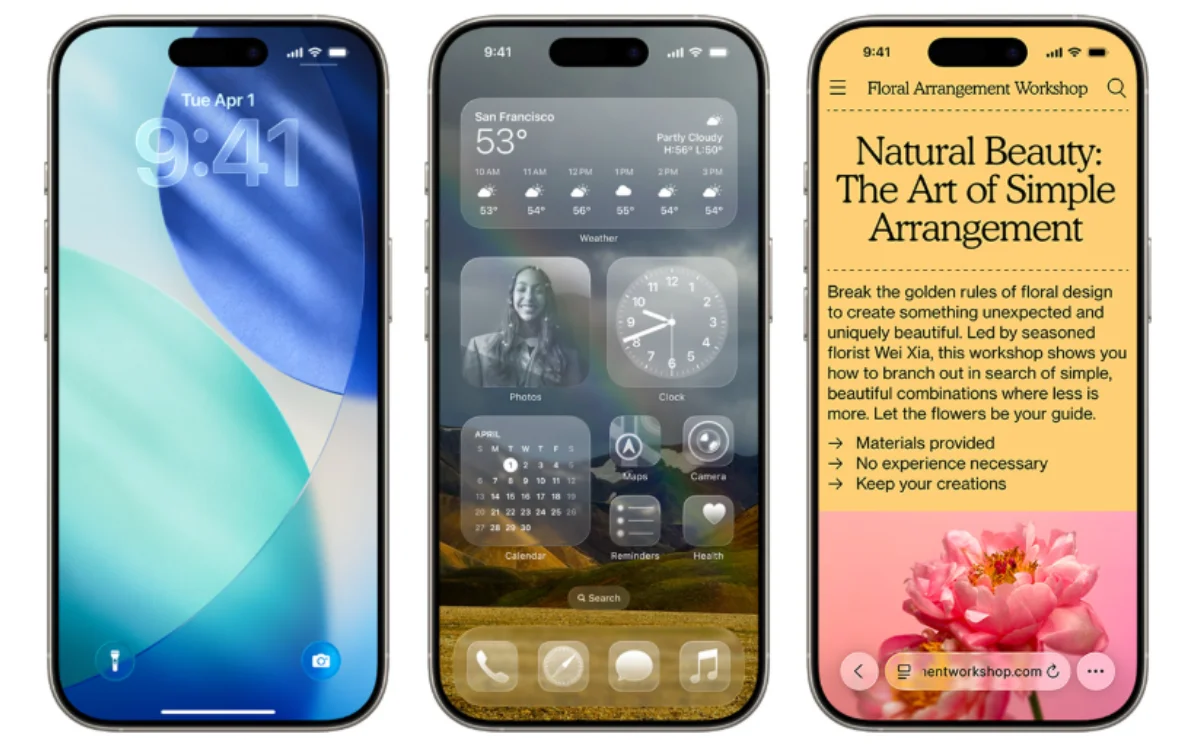
Find a serious enough flaw in iOS or Safari’s Lockdown Mode, and Apple might drop up to $5 million your way.
That’s not a typo – that’s five million dollars.
DISCOVER SBX CARS – The global premium auction platform powered by Supercar Blondie
The Apple Security Bounty program is offering an insane top prize
Starting this November, Apple’s Security Bounty program – that’s the official name for its find-a-bug, earn-some-cash system – is getting a massive upgrade.
The new top prize is $5 million, which is double the old prize, and it’s only for the toughest bugs on Earth.
We’re talking flaws that can sneak into Apple’s beta software or break through Lockdown Mode – a super-secure setting built to defend people from spyware.
Lockdown Mode exists to protect people like journalists and human rights workers from hackers who work for governments or spy agencies.
Apple says those ‘mercenary spyware’ attacks are the only real iPhone hacks it’s ever seen in the wild.
And it wants to stop them for good.
So, if someone can find a way around those defenses, Apple wants to hear about it before the bad guys do.
And instead of punishing you, they’ll pay you like a celebrity.
Smaller bugs, smaller fortunes
The smaller buggy stuff still pays big, though.
Apple’s offering $2 million for what it calls ‘zero-click’ exploits – hacks that don’t even need you to tap or click anything to work.
If your trick needs just one tap or a nearby connection, that’s worth $1 million.
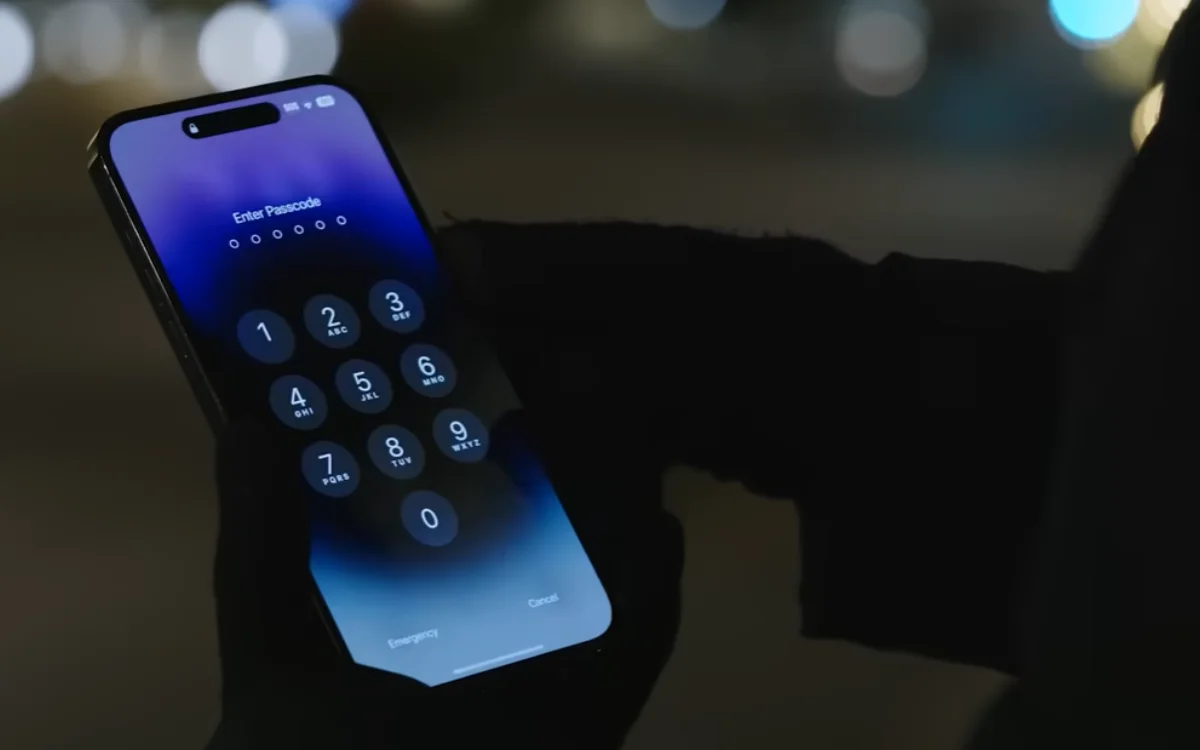
Even if your discovery needs you to actually hold the iPhone in your hands – like finding a way into a locked phone without the passcode – Apple will still pay $500,000.
And chaining bits of code together to escape Apple’s sandbox system gets you $300,000.
Apple’s head of security, Ivan Krstić, says the company’s already paid $35 million to over 800 researchers who’ve helped make its devices safer.
It’s all part of Apple’s plan to keep hackers busy finding bugs for the good guys, not selling them to the bad ones.
Because in 2025, catching a flaw in iOS might just make you richer than launching your own app.
With roles at TEXT Journal, Bowen Street Press, Onya Magazine, and Swine Magazine on her CV, Molly joined Supercar Blondie in June 2025 as a Junior Content Writer. Having experience across copyediting, proofreading, reference checking, and production, she brings accuracy, clarity, and audience focus to her stories spanning automotive, tech, and lifestyle news.